
Feature docs · AI security
If your site ships an AI chat, assistant, or model endpoint, you have a new attack surface. Guardbee AI modules inventory that surface, run safe canary checks, and report leakage signals in business language.
Modules
- AI Security Checks: chat widgets, vendors, and model endpoint signals
- Prompt Injection: harmless canary request against same-origin AI endpoints
- LLM Data Leakage: secrets and PII in AI-related content / crawl bodies
Business impact
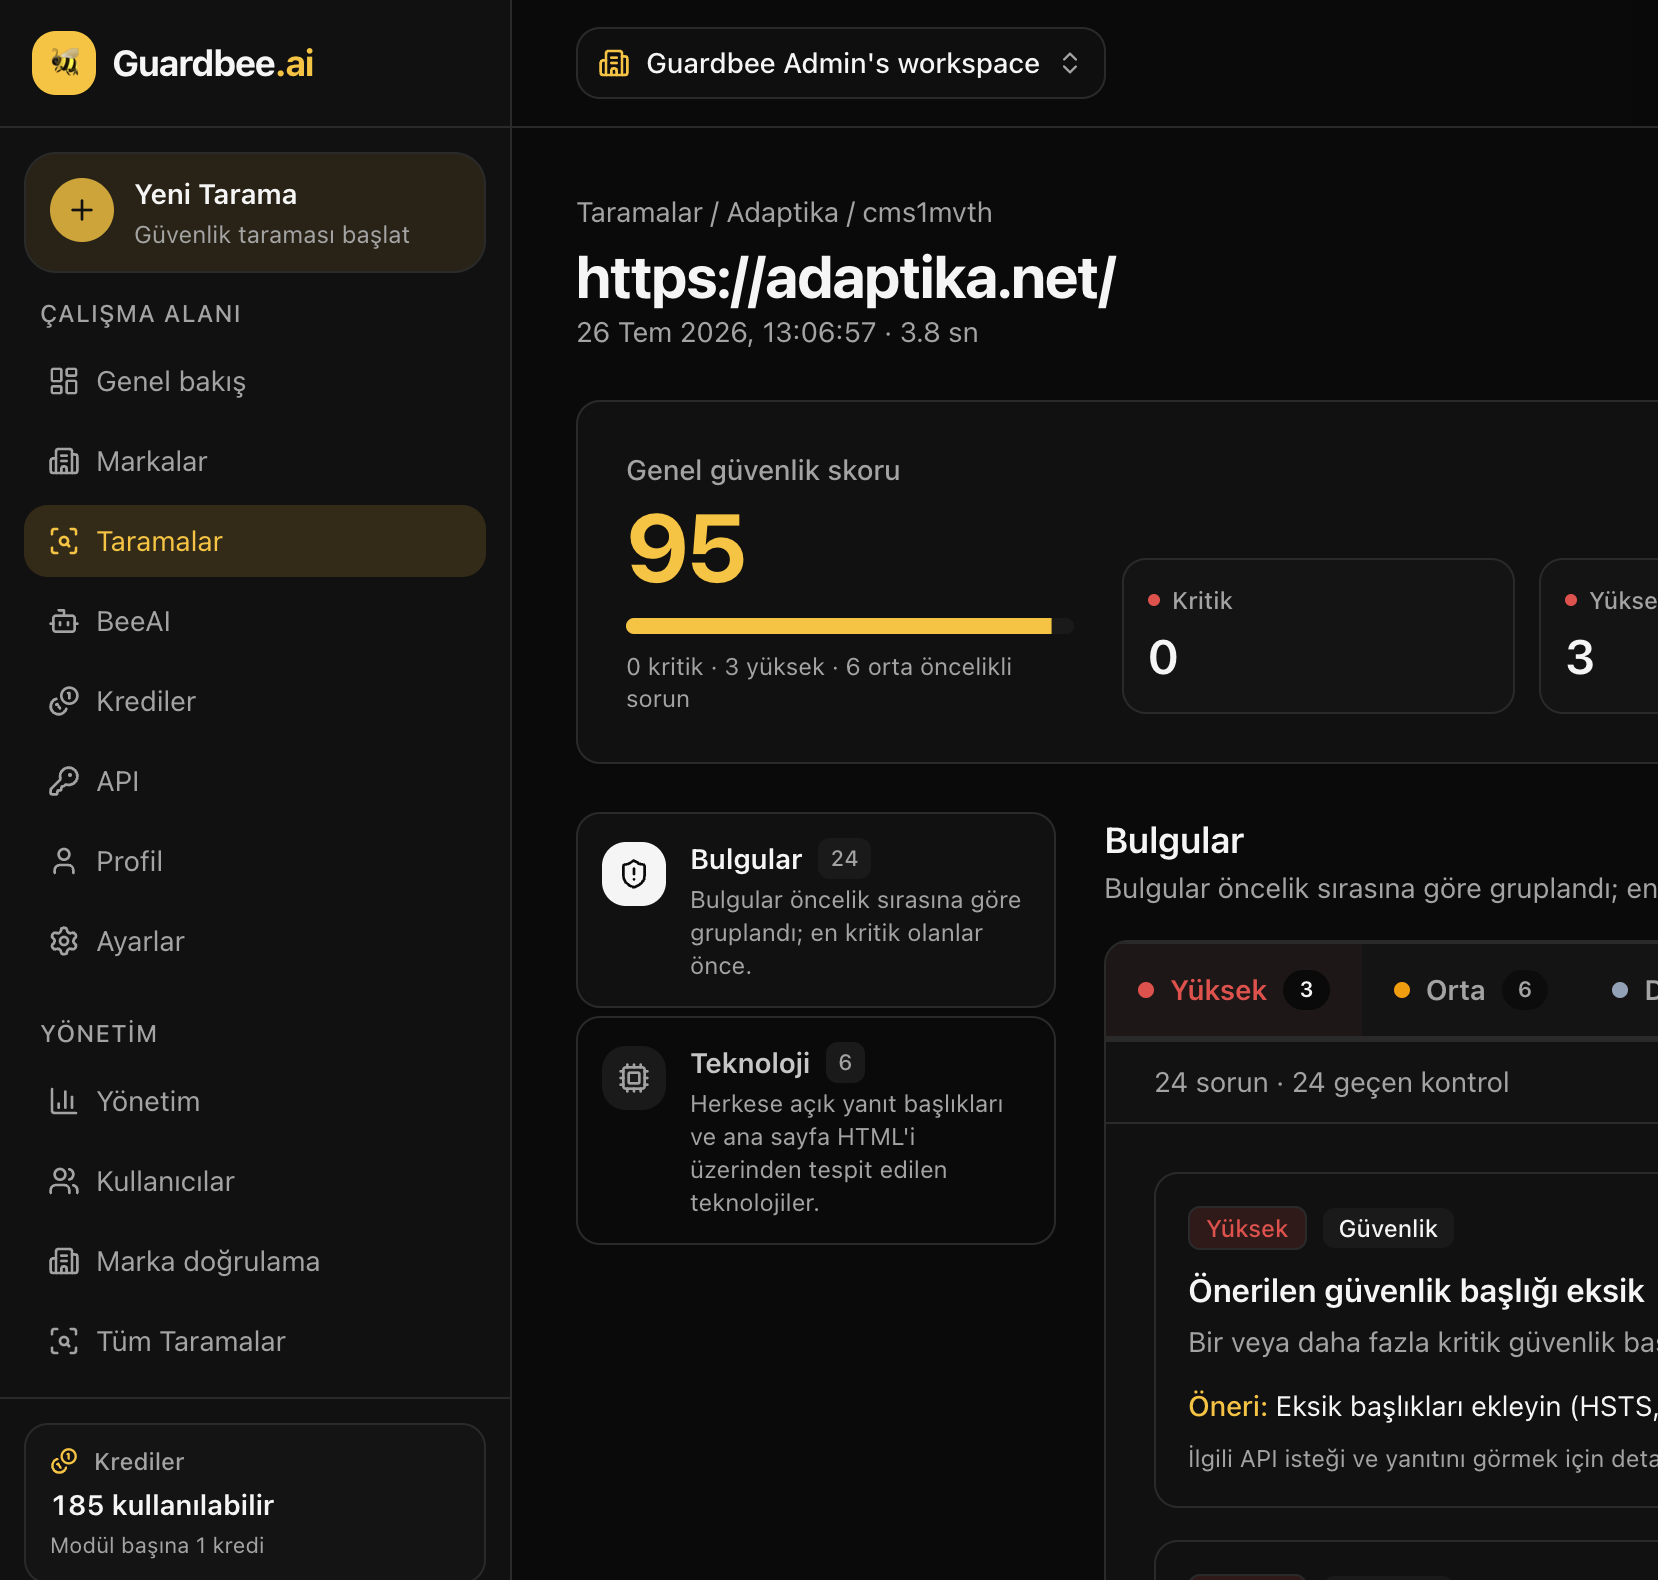
Prompt injection is not a curiosity — it affects brand trust, customer data, and support cost. Leaked API keys or personal data in model responses are compliance and trust crises. In board language: “We have AI — what is our visible risk?”
Related reading
Why AI security is now a board-level topic
Run these checks with Guardbee
Add your brand, pick the modules that matter, and get findings in business language. Start with a 14-day free trial.
Frequently asked questions
Is prompt-injection testing harmful?
No. Guardbee uses harmless canary requests — not destructive or attacker payloads.
Is BeeAI the same as AI scanning?
No. BeeAI explains findings; AI surface scanning is a separate module set.
Who should run these scans?
Any brand with a chatbot, assistant, RAG UI, or third-party AI widget.